
Industry
SaaS Security for the Public Sector
Secure the public sector by managing configurations, security posture, and drift across your SaaS environment.
How AppOmni secures SaaS
for Government
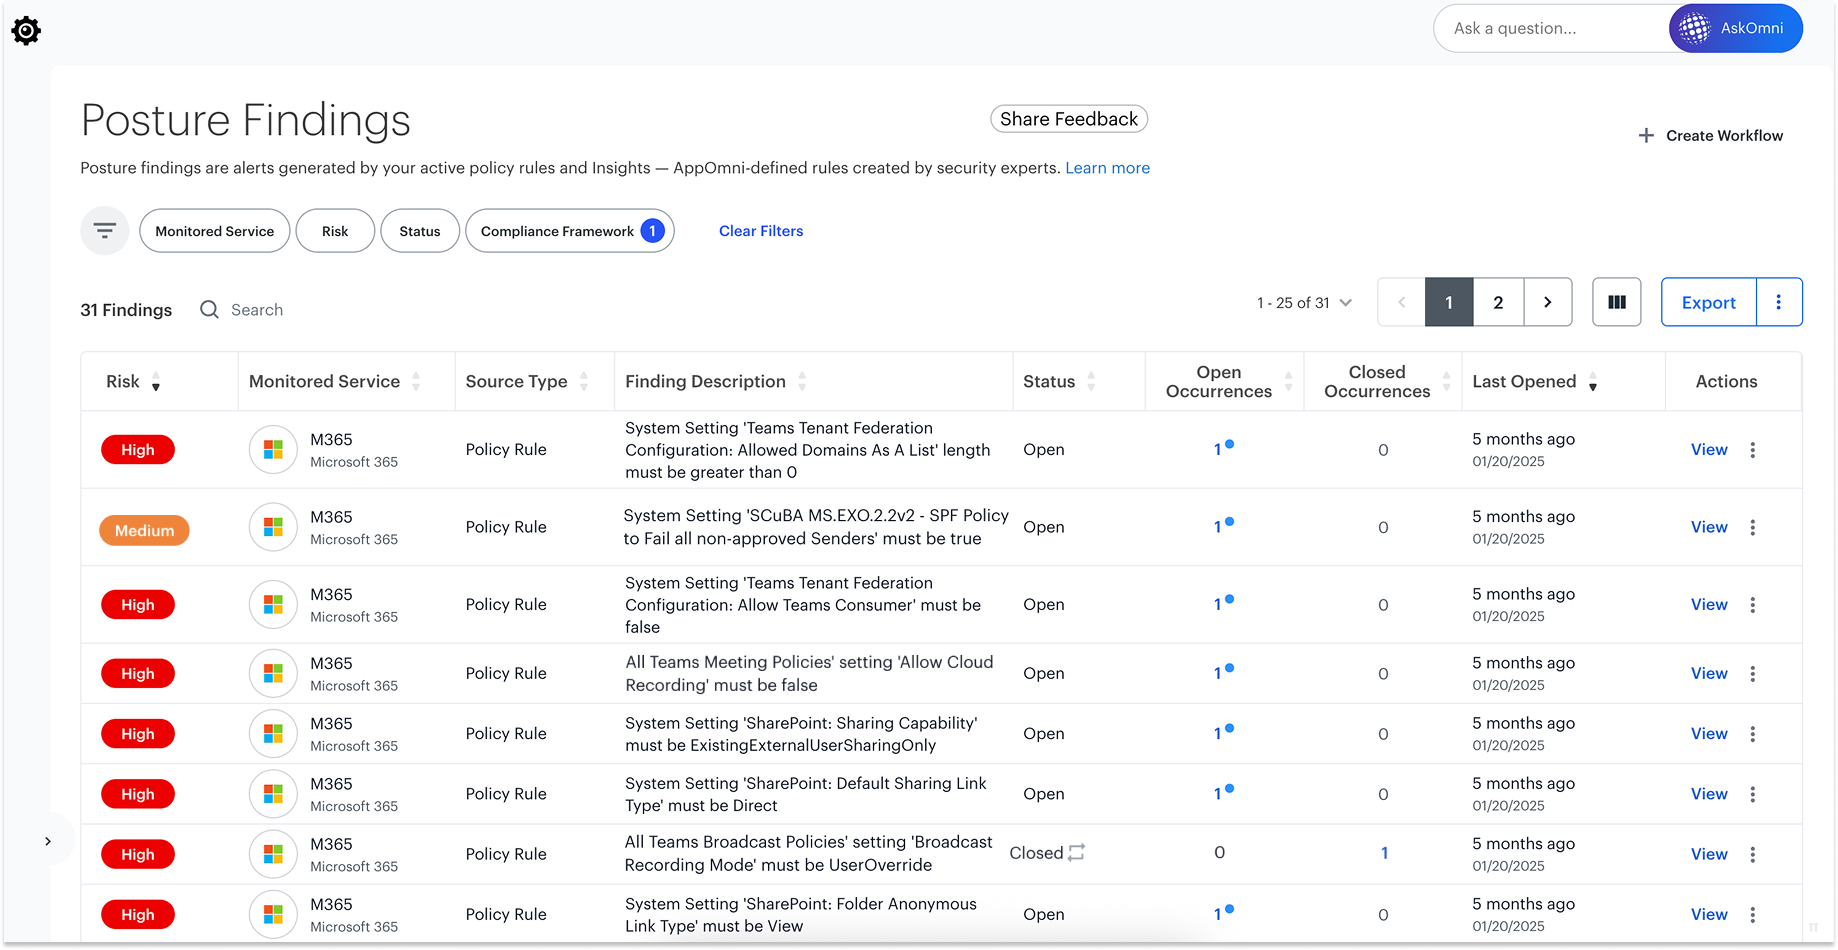
Misconfigurations, unauthorized access, and compliance requirements like SCuBA, NIST 800-53, and FISMA demand a proactive approach.
AppOmni delivers visibility, control, and compliance for SaaS applications, enabling government teams to protect sensitive data, meet stringent security frameworks, and streamline compliance reporting—all without disrupting operations.
Out-of-the-box Compliance Checks
Detect Configuration Deviations
Automate With Continuous Monitoring
Triage and Remediation Guidance
FedRAMP-Authorized SaaS Security for Federal Agencies
AppOmni’s SaaS Security Platform has been granted FedRAMP® Authority to Operate (ATO), giving federal agencies a trusted path to secure their SaaS environments with confidence. Backed by 325+ controls and built to meet the U.S. government’s highest cybersecurity standards, AppOmni supports agencies in safeguarding sensitive data like CUI, PII, and PHI across platforms like M365, Salesforce, and ServiceNow.
With CISA’s BOD 25-01 now in effect, AppOmni helps federal and civilian agencies, private enterprises, and highly-regulated industries meet SCuBA compliance requirements out of the box—providing instant visibility, secure configurations, and continuous monitoring across core Microsoft apps.


AppOmni on FedRAMP Marketplace
Latest Resources
-
ConnectWise Cloud Backup Compromise in Microsoft 365: What Happened and What to Do Now
Key Takeaways What happened to ConnectWise Cloud Backup, and who is affected? This is a supply-chain attack on a Microsoft 365 backup app. Attackers obtained a credential for ConnectWise Cloud Backup app (formerly SkyKick) and used it, as the app’s service principal (the identity an app uses inside a tenant), to sign in to customer…
-
Walk, Run, Fly: A Practical Framework for SaaS Security Prioritization
Learn how to prioritize the SaaS applications that matter most using a practical 80/20 framework to reduce risk, strengthen security, and build a scalable SaaS security program.
-
Top 7 AI Security Risks in SaaS Environments
Discover top agentic AI security risks in SaaS and practical ways to secure AI identities, data access, and agentic workflows.