SaaS Data Exposure
Automate and streamline SaaS data exposure activity and resolution.
CHALLENGE
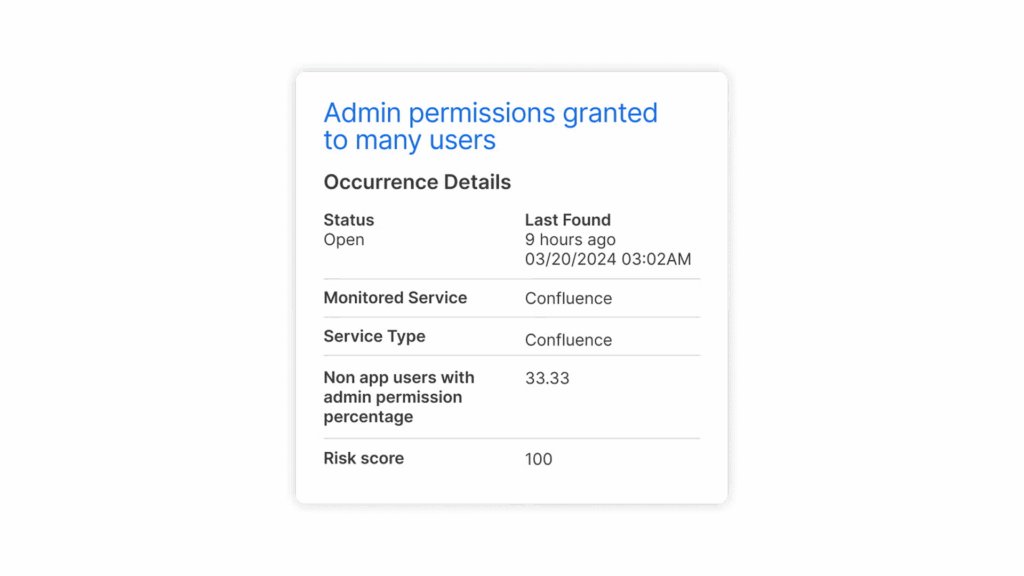
SaaS apps hold sensitive data, but access controls and sharing settings are often complex or misconfigured. A single mistake—like publicly shared data, excessive permissions, or a forgotten integration—can expose critical information. AppOmni centralizes SaaS monitoring and management to help keep your data secure.
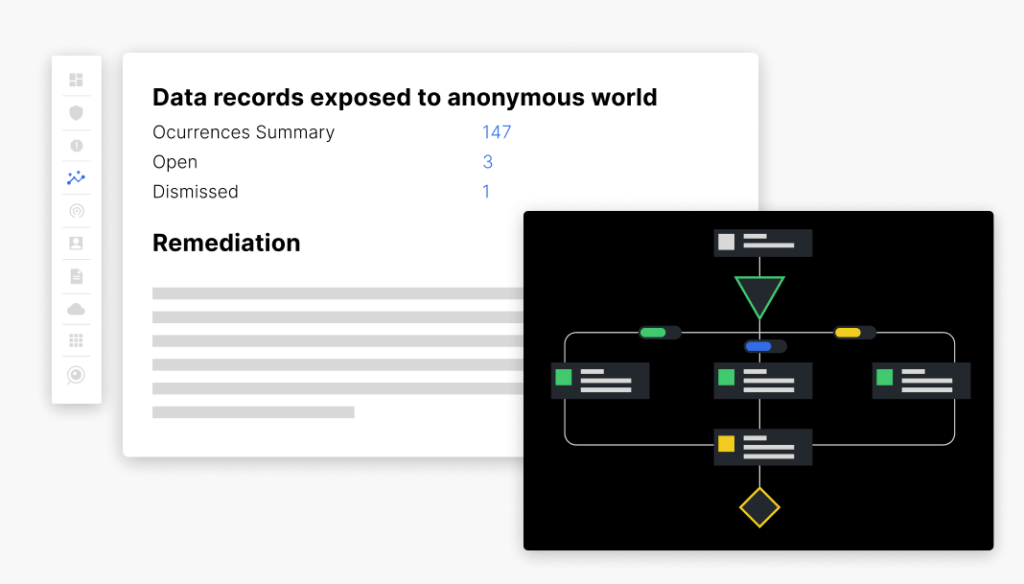
How AppOmni prevents SaaS data exposure

Reduce Your Attack Surface
Identify and prioritize remediation of vulnerabilities and misconfigurations that can lead to data exposure for SaaS.

Accelerate Remediation
Gain context and insight into potential exposures and fix them with guided remediation.

Access Exposure Controls
Define and monitor specific data access and permissions to investigate exposure risks.
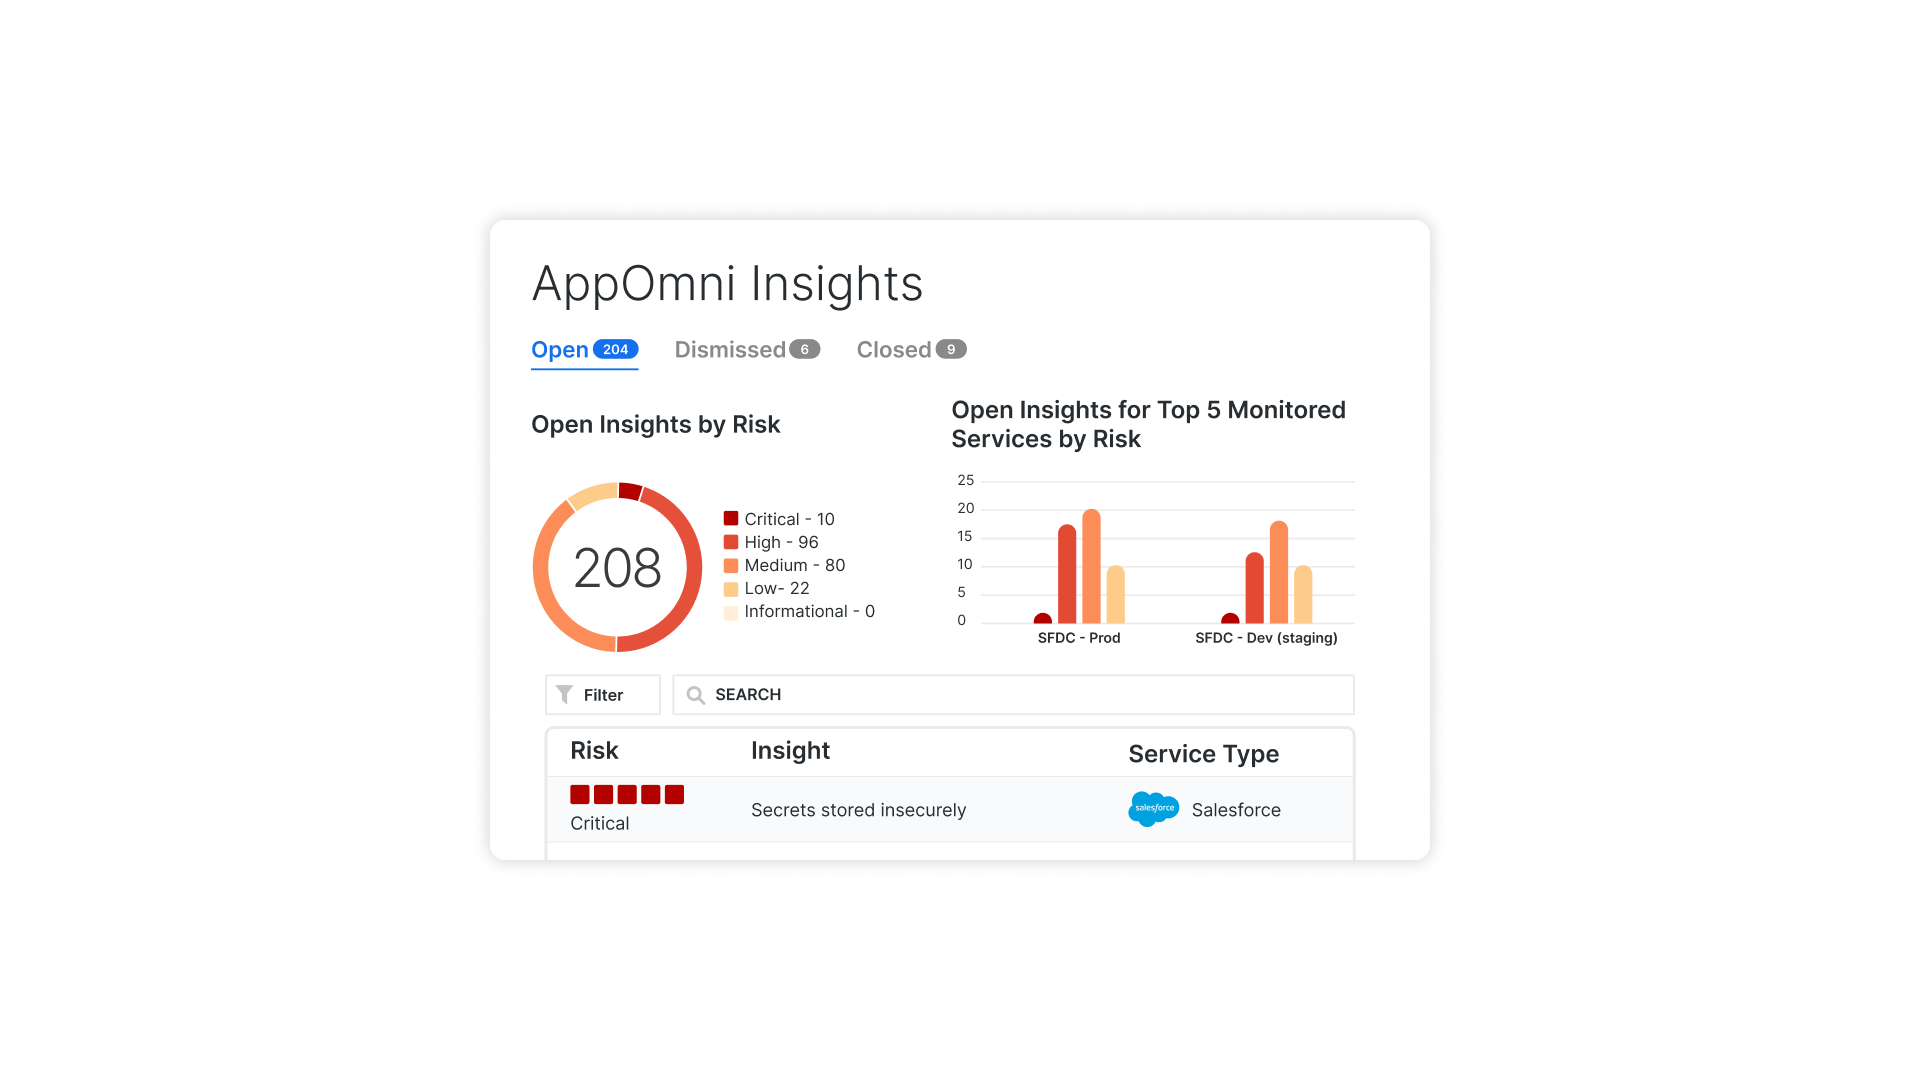
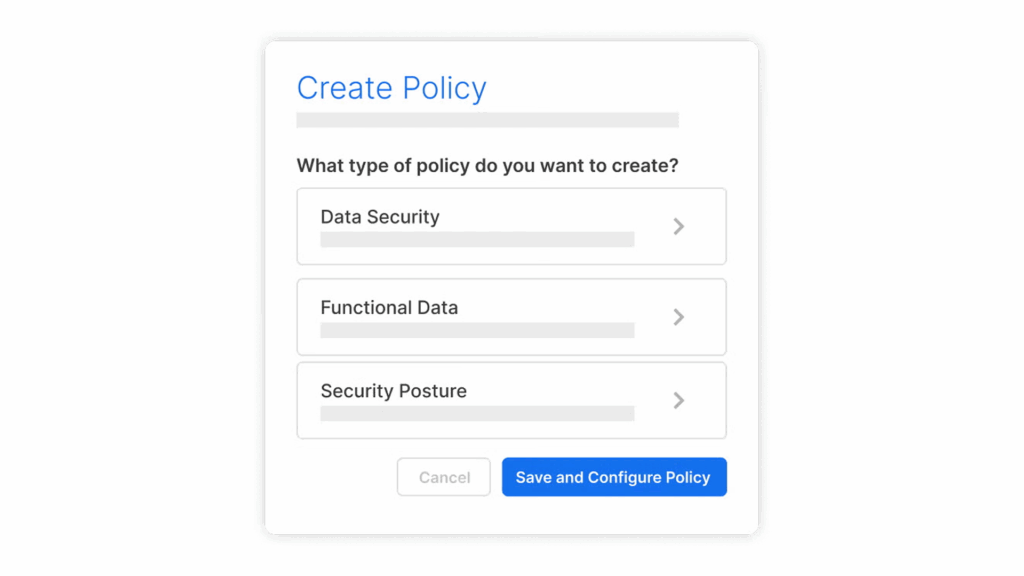
Key Features
Extensive Data Exposures Uncovered in ServiceNow Knowledge Bases
A recent investigation by an AppOmni SaaS Security Researcher revealed widespread data exposure risks in ServiceNow Knowledge Bases. Misconfigurations left over 1,000 enterprise instances open to unauthorized access.
Related Content
-
ConnectWise Cloud Backup Compromise in Microsoft 365: What Happened and What to Do Now
Key Takeaways What happened to ConnectWise Cloud Backup, and who is affected? This is a supply-chain attack on a Microsoft 365 backup app. Attackers obtained a credential for ConnectWise Cloud Backup app (formerly SkyKick) and used it, as the app’s service principal (the identity an app uses inside a tenant), to sign in to customer…
-
AI Security Starts with Visibility Into Your SaaS Environment
Can your security team see what data AI agents use, whose permissions they run under, and what they can do? Start with visibility into your SaaS environment.
-
Walk, Run, Fly: A Practical Framework for SaaS Security Prioritization
Learn how to prioritize the SaaS applications that matter most using a practical 80/20 framework to reduce risk, strengthen security, and build a scalable SaaS security program.
Critical applications secured
Protect data essential to your business

Microsoft 365

Salesforce

ServiceNow

Workday

Google Workspace
“I needed to get a better understanding of the overall attack surface, our portfolio of applications, and their configurations and data exposure risks.”
Wai Sheng Cheng
Information Security and Risk Manager, Spencer Fane